Skip to content
EliTechZ homeMenu
info@elitechz.comPulse101

01 / 04EliTechZ

Infrastructure + offensive security

Elite IT
A-Z.Cloud Infrastructure & Offensive Security

Infrastructure that performs.
Security that holds.

When a platform is unreliable or a security question keeps coming back, you need someone who can get into the detail and own the work. EliTechZ builds the fix, tests it and shows your team how to run it.
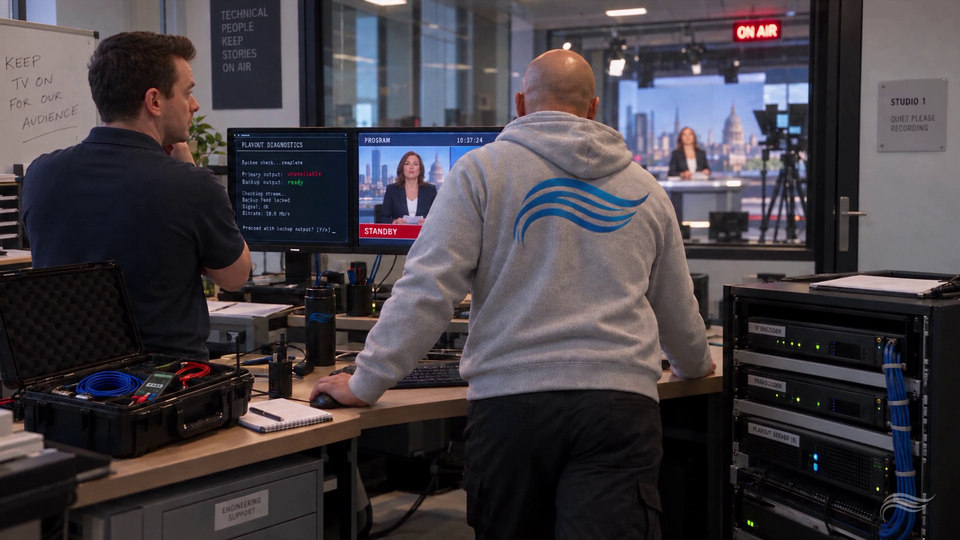
The EliTechZ storyCompany film
From pressure to progress.Sound on for the full story

Be in control. Keep the platform running without losing sight of cost or risk.

Explore the security perspective

Cloud infrastructure.
AI integration.
Offensive security.

A cloud migration or security redesign is hard to undo. We work through the trade-offs with your team before changing the platform, then test the result.

Your team should understand what changed and how to look after it. Our experience includes European e-commerce logistics, media, broadcast and streaming platforms.

Platforms that support the business
Cloud, on-premises or hybrid: the platform has to work on a difficult day, not just at launch. We account for access, networking, monitoring and recovery while building it.
AI integration & automation
AI should make a real task easier. We connect it to your workflow, limit what data it can reach and agree where a person needs to check the output.
Security built into delivery
Security is part of the build. We set sensible defaults, test what could go wrong and check that the changes actually help.
A solution your team can own
We build the platform, prove it works and explain it to the people who will run it. They should not have to call us just to understand the next change.
More about EliTechZ

Elite IT A-Z means staying with the work until your team can run the result. That might mean untangling a cloud platform or sorting out the basics, such as business WiFi, remote access or storage. We can discuss EU hosting and relevant GDPR or NIS2 requirements when they affect the design.
02 / 04Infrastructure

Cloud · platform · identity

Cloud & platform
engineering.

Resilient platforms.
Secure identity. Calm operations.

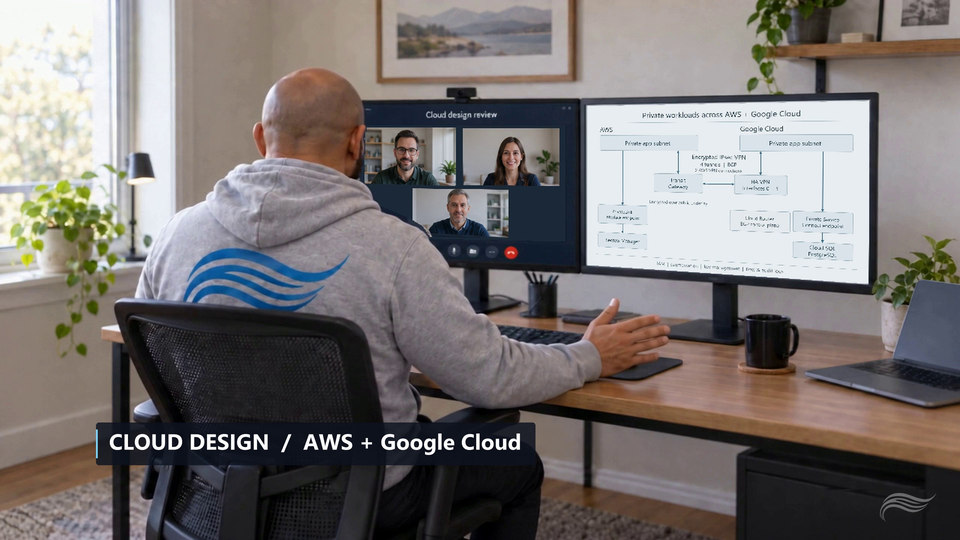
A platform can look sound on paper and still be painful to operate. We work across cloud, hybrid and on-premises systems, connecting identity, automation and monitoring to the way your team actually runs them. AI integration is considered where it solves a useful problem.

From complexity to controlInfrastructure film
Build. Automate. Observe. Improve.Sound on for the full story

Across your estate. AWS, Azure, GCP, Kubernetes, VMware, and Nutanix.

Start with your environment

Practical engineering.
From foundation to operation.

Start with the issue that is costing your team time. If it points to a wider problem, we can look at the architecture together.

Blue team & incident response
When an incident happens, the first job is to understand it. We use tools such as Microsoft Sentinel and KQL to investigate, then strengthen the controls that would help you spot or contain a repeat.
AI integration & workflow automation
We start with the task you want AI to improve, not the model you want to use. Once it is connected to your application, we check its output, restrict data access and make sure someone owns it after launch.
Kubernetes, migration & automation
Moving a workload is only useful if the new environment is easier to run. We build cloud foundations and Kubernetes platforms on AKS, EKS, GKE or on-premises systems, using Terraform, Ansible and Helm to make changes repeatable.
Nutanix & VMware vSphere
If your Nutanix or VMware vSphere estate is due for a refresh, we look at what the workloads need before changing it. That includes how the platform performs, how it recovers and how your team will maintain it.
Workplace & connectivity
Workplace changes should not leave people locked out or your support team guessing. We help with Microsoft 365 and Google Workspace migrations, along with the networks, WiFi and remote access people rely on each day.
CCTV, access control & building systems
CCTV and door-access systems need reliable networks and storage. We help keep them separate from general business traffic and make maintenance access deliberate rather than always open.
Monitoring, observability & FinOps
A dashboard is useful only when someone knows what to do with it. We use Grafana, Prometheus and Loki to make problems visible, tune alerts to reduce noise and relate the signals to reliability and cloud spend.
Backup & disaster recovery
A backup is not a recovery plan until someone has restored from it. We check capacity and storage performance, design for failure and test whether the restore works as expected.

Case studies

These examples show the kind of work we have done. Client details are omitted, and results will differ in your environment.

Active Directory hardening

Challenge: Older authentication was still in use, and service accounts carried more access than they needed.

Approach: We moved services off NTLMv1, then disabled NTLMv1 authentication. Service accounts were converted to group Managed Service Accounts (gMSAs). Where a writable domain controller was not needed, we used a read-only one, and we raised the functional level to Windows Server 2025. We also separated storage and client settings in Group Policy and replaced startup scripts with policy-based configuration.

Result: Less reliance on legacy authentication and shared passwords. The new Group Policy structure is easier for the team to understand and maintain.

Zero-trust microsegmentation

Challenge: Services could reach parts of the network they had no reason to talk to. That made a single breach harder to contain.

Approach: We put zero-trust controls at the front end and limited each microservice to the data services it actually needed. Terraform and Kubernetes made the boundaries repeatable. Monitoring and security reporting still had to work after the change.

Result: Services had fewer unnecessary network paths. Broadcast traffic fell, and the team kept the visibility it needed to operate the platform.

Azure network performance

Challenge: Network performance on the Azure virtual machines was holding production back.

Approach: We updated the NIC drivers across the estate to supported versions and tuned MTU settings, including jumbo frames where appropriate.

Result: Production speed improved by a further 22% in that environment.

From assessment to a platform you can operate

We start by asking what the business depends on, what breaks today and what a longer outage would cost. That gives us a sensible order for the work.

The work might be a migration, an automated build or a better way to monitor an existing platform. Before we leave, your team knows what changed, who gets the alerts and how to check recovery.

CCTV and connected building security

A camera is no use if its recording network or storage fails. We look at the infrastructure behind CCTV and door access, including what happens when power or connectivity is lost.

We keep building systems apart from ordinary office traffic and agree who can access recordings or maintain devices. Retention and recovery are discussed with the building owner and relevant specialists.

Platforms and specialist capabilities

Older systems and newer cloud services often have to coexist. We help teams update Windows 11 endpoints and Windows Server 2025 estates, harden tenant access and move between Microsoft 365 and Google Workspace.

For Kubernetes, we work with AKS, EKS, GKE and Nutanix Kubernetes Platform. Terraform, Ansible and Helm help your team repeat a change safely. We also work on detection, segmentation and email authentication when those are the real gaps.

If EU hosting, GDPR or NIS2 affects your choices, we bring those requirements into the conversation early, alongside recovery and cost.

  • Cloud architecture (AWS / Azure / GCP)
  • Kubernetes platform engineering
  • Terraform / Infrastructure as Code
  • CI/CD & GitHub workflows
  • Hybrid cloud (Nutanix)
  • On-prem: VMware / vSphere / ESXi
  • Identity: IAM / AD / Conditional Access
  • Zero Trust principles
  • Endpoint management (Intune / MDM)
  • Network security & segmentation
  • Firewalls & secure connectivity
  • Observability & incident readiness
  • SRE reliability practices
  • FinOps cost optimization
  • Microsoft 365 / Office 365 administration
  • Google Workspace administration
  • M365 & Workspace migrations (tenant/platform)
  • Email & identity modernisation
Qualifications and professional recognition

Individual engineering portfolio on GitHub. Public responsible disclosure acknowledgements are listed in the Red Team section.

Individual qualifications

Qualifications earned by the engineer delivering EliTechZ services include ISC2 Certified in Cybersecurity, Microsoft Certified: Azure Fundamentals (AZ-900), ITIL Foundation, and Nutanix Associate and Professional certifications covering multicloud infrastructure, cloud integration, business continuity, and network security.

Earlier achievements include PRINCE2 Foundation in 2019 and Microsoft Windows 7 specialist certifications in desktop support and configuration in 2015.

Training and professional recognition

Completed Architecting on AWS and Migrating to AWS courses, plus Syberwise ICS security learning through beginner and intermediate quiz levels.

Individual professional recognition includes Maersk STARS and SPOT awards for customer support, collaboration, and problem solving.

The experience behind EliTechZ includes responsible vulnerability disclosures acknowledged by NCSC-NL and an April 2026 SPOT award for identifying and responding to a significant security threat.

Platform updates and source feeds

The latest items from the Kubernetes, GitHub Docs and Proxmox release feeds, refreshed daily. Each entry keeps its original publication date and links to the source, with the feed’s licence noted beneath it.

03 / 04Red Team

Offensive security · vulnerability testing

Penetration testing.
Red teaming.

Offensive security that gives
your team a clear next step.

Penetration testing should tell you what someone could actually reach, not just produce a list of warnings. We test the agreed systems, explain what we could demonstrate and help your team decide what to fix first.

A different perspective on riskSecurity film
Test the path. Validate the impact.Sound on for the full story

Evidence that leads to action. See what was found, why it matters and whether the fix holds.

Define the scope together

Understand the exposure.
Know where to act.

We follow realistic attack paths within the agreed scope. The report should make sense to the engineer fixing the issue and the person deciding what to tackle first.

Current red teaming client: Freudiger IT Security.

Web, API & cloud
We test whether a flaw in a web app, API or cloud service could lead to something important. Findings are ranked by what we could demonstrate, not by a generic severity label alone.
AI penetration testing
An AI feature may handle untrusted text or have access to tools it does not need. We test those boundaries, explain the risk and check the changes when a retest is agreed.
Identity & Active Directory
Identity controls matter most when an ordinary account is compromised. We look for routes to wider access in IAM and Active Directory, then check whether hardening closes them.
Applications, binaries & mobile
We examine how an application handles access and stores data, including what can be learned from its binaries or mobile app. The report tells your developers what needs attention.
Device & hardware security
For routers and embedded devices, we agree what can be tested before touching the hardware. The depth of a firmware or chip-level review depends on the device and the permissions available.
Physical & building security
A physical review looks at the agreed building and how access works in practice. That may include visitor entry, CCTV coverage and who responds when something goes wrong.
Deliverables that support decisions
You get a plain-English account of what we found and why it matters, backed by evidence your team can use. We agree what to fix first and can retest the changes.

Case studies

These examples show the kind of work we have done. Client details are omitted, and results will differ in your environment.

Lost-device resilience assessment

Challenge: The question was simple: what would be exposed if a managed laptop was left behind?

Approach: We tested the device and followed the access available from it, checking whether monitoring would alert the team and whether cloud files stayed protected.

Result: On-demand file controls limited access to user data. Monitoring and application permissions needed attention, so the team received a clear order for the fixes.

Azure third-party access assessment

Challenge: The organization had put strong controls around its own Azure accounts. It wanted to know whether outside support access was held to the same standard.

Approach: We reviewed the agreed Azure environment, including how its IT partner could reach supported services.

Result: The internal controls held up well. A third-party support route needed tighter access controls.

AI application: recruitment platform

Challenge: A recruitment team used an LLM to turn CVs into short summaries.

Approach: We checked what happened when the application passed untrusted CV content to the model.

Result: The content changed the summaries in ways the team did not expect. We recommended clearer input boundaries and a person checking the result.

How an assessment is scoped and verified

Before testing, we agree exactly what is in scope and what is off limits. That includes the systems, permissions, timing and any risk to live operations.

The report shows what we tested, what happened and how to address it. Your team can see which issues matter most. If a retest is part of the agreement, we check whether the fix holds.

For a building review, we agree the boundaries with the owner before visiting. We then look at how entry, cameras and connected devices work together, and who is expected to respond.

Public profiles and responsible disclosure

Responsible disclosure acknowledgements

Responsible disclosure work by the engineer behind EliTechZ is acknowledged on the following organisations' public pages. These are individual research acknowledgements.

Oasen · DMC Group · Netherlands Tax Administration · Microsoft Security Response Center · Utrecht University · Wageningen University & Research · Lentiz · TU Delft.

Individual NASA appreciation letters received in 2024 also recognise responsible vulnerability disclosure.

Security research and continuous learning

Bugcrowd research profile · TryHackMe training profile.

Hands-on practice includes security labs and CTFs. The public profiles provide a view of ongoing activity.

Security advisories and source feeds

The latest advisories from the NVD, CERT-EU and NCSC feeds, refreshed daily. Each entry keeps its original publication date and links to the source, with the feed’s licence noted beneath it.

04 / 04Contact

Based in Hilversum · Netherlands + worldwide support

Be in control.
Start a conversation.

Tell us what is getting in the way.

You do not need a finished project plan. Tell us what is not working, what you have tried and what a good outcome would look like.

The simplest way to begin

info@elitechz.com

A short email is enough. Tell us what is happening, which systems are involved and when you need help. Please leave passwords and sensitive data out of the first message.

Lijsterweg 65 · 1221JH HilversumKVK 93985290Google Maps · OpenStreetMap

Infrastructure. Security. Delivery. A connected view of the work ahead.

Revisit the EliTechZ story

Bring the question
that matters to your team.

You can start with a problem, not a project plan.

A platform needs attention
Perhaps the platform slows down at busy times, or the same incident keeps returning. Tell us what happens and when.
A migration is coming
Moving to cloud or changing identity systems affects the people who use them. We can help plan the move without losing control of access or costs.
Security needs evidence
If you are unsure whether a control works, we can test it within agreed boundaries. You will know what to fix and whether the change helped.

How an engagement works

A clear start, regular updates and a handover your team can use.

1. Scope
We agree what needs to change, what is in scope and what your team will receive. For security testing, written permission comes first.
2. Deliver
We do the agreed work and keep your team informed, especially if a finding changes the plan.
3. Validate
We check whether the change solved the problem and show you how we reached that conclusion.
4. Handover or retest
Your team gets what it needs to run the result. For security findings, we can test the fix again if that is part of the scope.

Frequently asked questions

Need help? Email info@elitechz.com.

What should I include in an enquiry?

Tell us what is happening, which systems are affected and when you need help. Please do not send passwords or sensitive data in your first email.

Why do you use email instead of a contact form?

There is no contact form, analytics or advertising tracking. Email us when you choose to. Cloudflare processes essential request data to deliver and protect the site.

How are scope and timelines agreed?

We put the work, price and timing in writing before we start. A security assessment also needs your explicit permission and clear limits.

How is confidential information handled?

We agree how to handle sensitive information before the work starts. If you need to send an encrypted security report, use the published PGP key and email security@elitechz.com.

What does infrastructure delivery include?

It depends on what you need. We might build a new platform, fix an existing one or automate a task that keeps causing trouble. We test the result and make sure your team knows how to run it.

What does a security assessment deliver?

You get a clear account of what we found, why it matters and what to fix first. The technical detail is there for the people doing the work.

Can security findings be retested?

Yes, if it is part of the agreed work. We test the affected area again to see whether the original issue is resolved.

Can you work alongside our existing IT partner?

Yes. We agree who does what with your team and your provider before work begins.

Do you work outside the Netherlands?

Yes. We are based in Hilversum and work with teams in the Netherlands and elsewhere. We can discuss the project in English or Dutch.

Chromium HSTS preloadMozilla HTTP Observatory GradeW3C ValidationUptime Robot ratio (30 days)

EliTechZ · Company film

The EliTechZ story

Close film: company film and return to home

Pause before closing. Sound, captions and fullscreen are available in the player controls.

EliTechZ · Infrastructure film

From complexity to control

Close film: infrastructure film and return to infra

Pause before closing. Sound, captions and fullscreen are available in the player controls.

EliTechZ · Security film

A different perspective on risk

Close film: security film and return to redteam

Pause before closing. Sound, captions and fullscreen are available in the player controls.